Trust-based electronic signature
Enable document signing with pre-verified identities and device trust assessment
Enables document signing for users who already have verified AML identity data, while intelligently adapting the flow based on device trust signals to balance security and user experience.
In this recommended flow, the customer’s system uses existing AML-compliant identity data from a previous verification to issue a signature without requiring users to repeat full identity proofing. Before the signature is created, the platform performs a device trust assessment, evaluating behavioral and technical signals to determine whether the device and network environment appear safe.
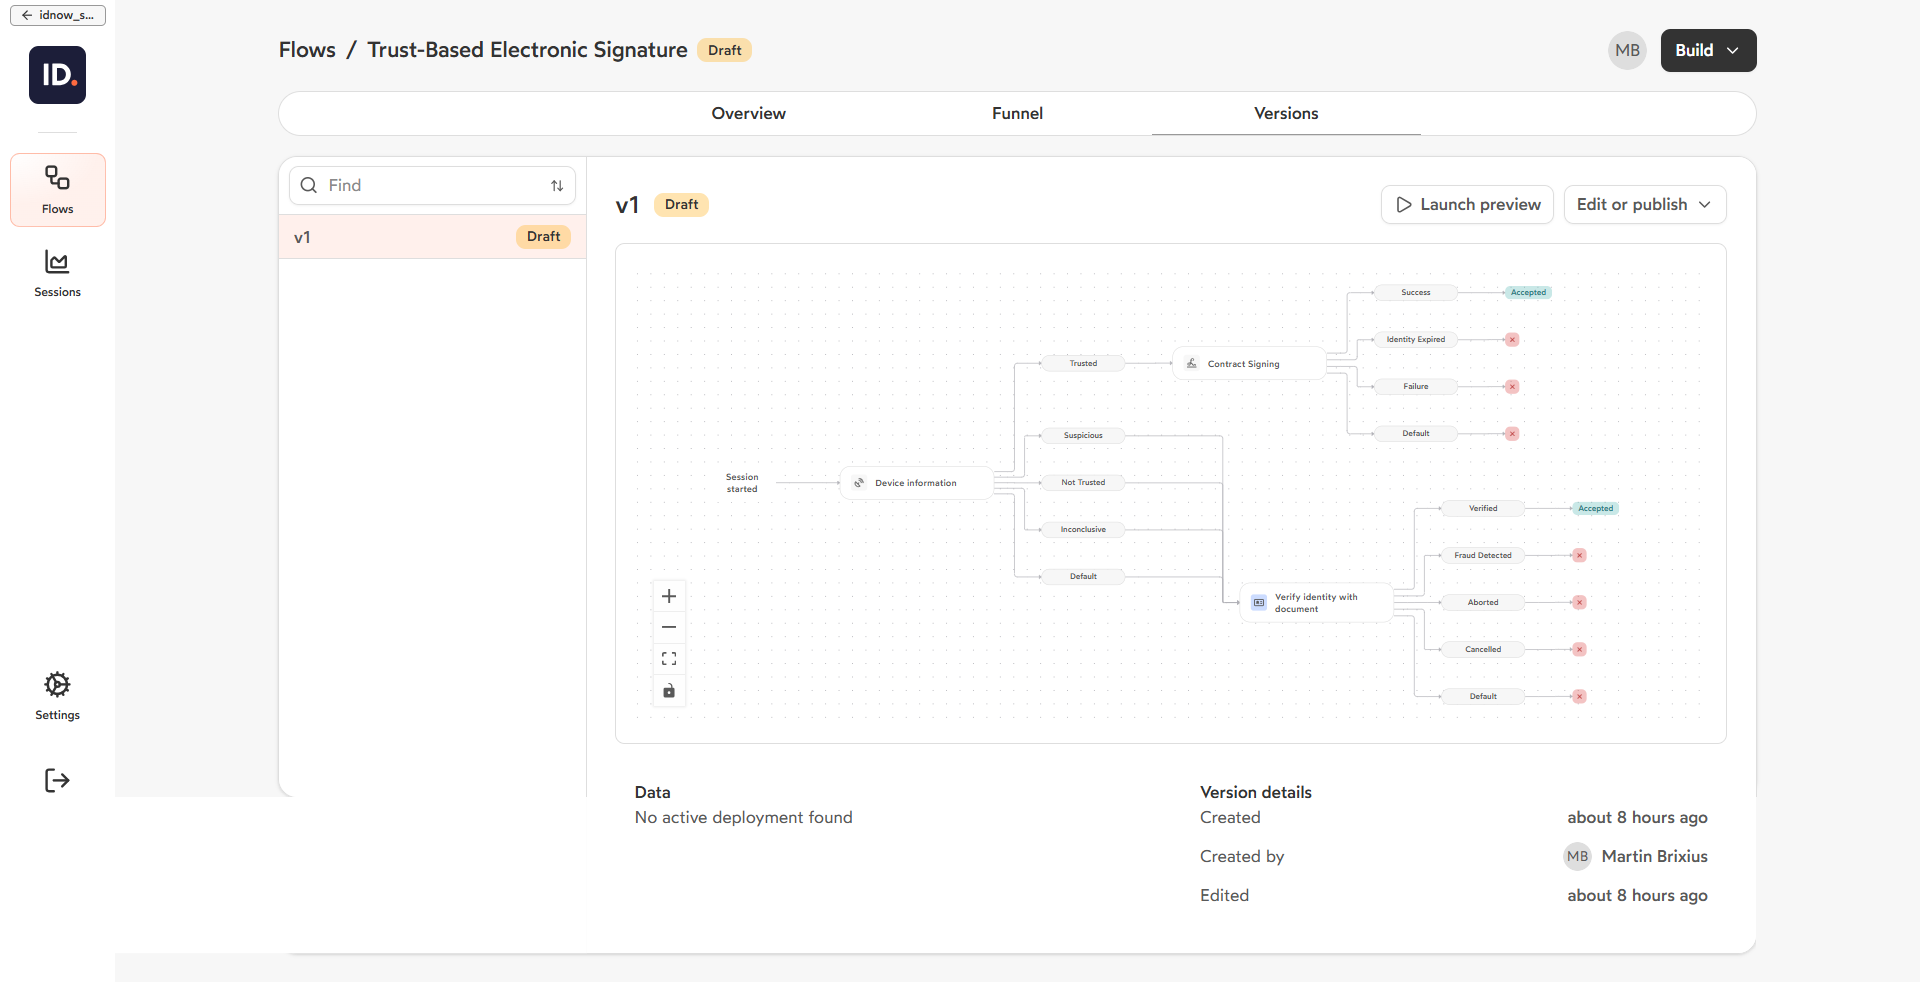
If the environment is trusted, the process continues seamlessly using the stored identity data. If the environment is suspicious or untrusted, the flow introduces a light dynamic verification step, prompting the user to provide a fresh set of identity evidence before continuing to issue a signature. This adaptive approach applies “healthy friction” only when risk is detected, ensuring compliance and fraud prevention while maintaining a smooth experience for low-risk users.
This trust-based signature flow helps organizations optimize security, compliance, and user experience, protecting against identity misuse and device-based fraud while keeping high completion rates.
Key benefits
- Adaptive trust decisioning – Dynamically routes sessions based on device and network risk signals.
- Frictionless experience for trusted users – Enables immediate signing using existing AML identity data.
- Healthy friction for suspicious sessions – Requests renewed verification only when anomalies are detected.
- Optimized risk and UX balance – Strengthens fraud prevention without compromising conversion.
- Compliance-ready – Maintains alignment with AML and eIDAS requirements for secure electronic signatures.
Flow Logic
Step overview
| Step | Purpose |
|---|---|
1. Start | Entry point; collects input data blocks |
2. Device signals | Analyzes device trustworthiness |
3a. Signing | Enables document signing (trusted path) |
3b. Verifying ID document (IDC) | Verifies identity via document capture (untrusted path). If successful, continues with step 3a. |
4. End | Final decision: accepted or rejected |
Routing
This flow uses a risk-based routing mechanism where routes at each step determine the next action. Trusted devices proceed directly to signing, while untrusted or suspicious devices require additional identity verification.
| Step | Route | Meaning | Action |
|---|---|---|---|
| Device signals | trusted | Device recognised, normal behaviour | Proceed to Signing |
| Device signals | suspicious, not_trusted, inconclusive | Unknown device or anomalies detected | Route to Verifying ID document (IDC) |
| Signing | success | Signing completed successfully | Session outcome accepted |
| Signing | identity_expired | Pre-verified identity exceeded validity period | Session outcome rejected |
| Signing | failure | Signature process failed due to technical error | Session outcome rejected |
| Verifying ID document (IDC) | verified | Identity confirmed via document capture | Continue to Signing |
| Verifying ID document (IDC) | fraud_detected, not_verified | Fraud or verification failure | Session outcome rejected |
Configuration
Device signals
| Parameter | Type | Description |
|---|---|---|
suspiciousUserThreshold | integer (≥0) | Threshold for "suspicious" classification based on suspectScore |
notTrustedUserThreshold | integer (≥0) | Threshold for "not_trusted" classification based on suspectScore |
confidenceScoreThreshold | integer (0-100) | Minimum fingerprint confidence; below this value result is "inconclusive" |
Example:
{
  "suspiciousUserThreshold": 50,
  "notTrustedUserThreshold": 75,
  "confidenceScoreThreshold": 60
}
Signing
| Parameter | Type | Description |
|---|---|---|
signingConfiguration.signatureLevel | enum | QES or AES (required) |
Signature levels:
| Level | Legal effect | Required input data blocks |
|---|---|---|
| QES | Equivalent to handwritten signature (eIDAS). Requires strict identity verification. | basicIdentity, documentData, documentsToSign |
| AES | Uniquely linked to signer. No regulated identity-proofing required. | basicIdentity, documentsToSign |
Example:
{
  "signingConfiguration": {
    "signatureLevel": "QES"
  }
}
Input data blocks
Provide these data blocks when creating a session:
| Data block type | Description | Required For |
|---|---|---|
basicIdentity | Pre-verified identity data | All flows |
documentData | Identity document information | QES signature level |
documentsToSign | Documents requiring signature | All flows |
Note: deviceSignals are auto-collected by Trust Platform.
Output data blocks
Trusted device path
When device signals indicate high trust and signature succeeds:
| Data block type | Created By | Description |
|---|---|---|
deviceSignals | Device signals | Device trust assessment results |
signedDocumentsPackage | Signing | Signed documents and metadata |
Untrusted Device Path
When device signals trigger identity re-verification:
| Data block type | Created By Step | Description |
|---|---|---|
deviceSignals | Device signals | Device trust assessment results |
documentImages | Verifying ID document (IDC) | Uploaded document images |
documentData | Verifying ID document (IDC) | Extracted document data |
extendedIdentity | Verifying ID document (IDC) | Verified identity data |
biometricSamples | Verifying ID document (IDC) | Liveness/selfie capture |
verification | Verifying ID document (IDC) | Verification results |
signedDocumentsPackage | Signing | Signed documents and metadata |
documentImages, documentData, extendedIdentity, and biometricSamples are only produced when the Verifying ID document (IDC) step reaches the verified route. If the step exits via not_verified or fraud_detected, only a verification data block is produced and the session ends with rejected — no signing step is reached.
API integration example
Scenario: Trusted device completes signature successfully
1. Create session
Request: POST /api/v1/flows/{flowId}/{environment}/sessions
{
  "input": {
    "basicIdentity": {
      "familyName": "Schmidt",
      "givenName": "Max",
      "birthDate": "1985-08-22"
    },
    "documentData": {
      "documentType": "ID",
      "documentNumber": "T22000126",
      "issuanceDate": "2020-05-10",
      "expiryDate": "2030-05-10",
      "issuingCountry": "DE"
    },
    "documentsToSign": {
      "documents": [
        {
          "templateId": "tmpl_loan_agreement_v2",
          "source": {
            "$ref": "vault",
            "$id": "a1b2c3d4-e5f6-7890-abcd-ef1234567890"
          }
        }
      ]
    }
  },
  "metadata": {
    "subjectId": "customer_ref_12345"
  }
}
2. Check session status
Request: GET /api/v1/{environment}/sessions/sess_abc123
Response:
{
  "flowId": "40cbb7b3-7468-4b5d-8bb5-ff8e82510c70",
  "flowVersion": 1,
  "environment": "live",
  "subjectId": "customer_ref_12345",
  "sessionId": "sess_abc123",
  "sessionStatus": "COMPLETED",
  "createdAt": "2025-12-18T10:30:00Z",
  "startedAt": "2025-12-18T10:30:15Z",
  "updatedAt": "2025-12-18T10:32:45Z",
  "completedAt": "2025-12-18T10:32:45Z",
  "expiresAt": "2025-12-18T22:30:00Z",
  "outcome": "accepted",
  "lastStep": {
    "stepId": "END",
    "stepType": "end",
    "stepDescription": "End step",
    "verdict": "accepted"
  }
}
3. Retrieve Data blocks
Request: GET /api/v1/{environment}/sessions/sess_abc123/datablocks
Response:
{
  "dataBlocks": [
    {
      "dataBlockId": "b1c2d3e4-f5a6-7890-bcde-f12345678901",
      "type": "deviceSignals",
      "createdBy": {
        "stepId": "device_signals",
        "clock": 1
      },
      "createdAt": "2025-12-18T10:30:18Z",
      "status": "STORED",
      "content": {
        "userReference": "customer_ref_12345",
        "provider": "Fingerprint",
        "timestamp": "2025-12-18T10:30:18Z",
        "result": "trusted",
        "browser": {
          "userAgent": "Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36",
          "incognito": false,
          "name": "Chrome",
          "version": "120.0",
          "os": "Windows 11",
          "deviceType": "desktop"
        },
        "network": {
          "ip": "192.168.1.100",
          "location": {
            "country": "DE",
            "city": "Berlin",
            "latitude": 52.52,
            "longitude": 13.405
          },
          "timezone": "Europe/Berlin"
        },
        "signals": {
          "deviceId": "dev_xyz789abc",
          "vpnDetected": false
        }
      }
    },
    {
      "dataBlockId": "c2d3e4f5-a6b7-8901-cdef-g23456789012",
      "type": "signedDocumentsPackage",
      "createdBy": {
        "stepId": "instant_signature_issuance",
        "clock": 2
      },
      "createdAt": "2025-12-18T10:32:45Z",
      "status": "STORED",
      "content": {
        "signatureProcessId": "tx_987654321",
        "signedDocuments": {
          "mode": "both",
          "archive": {
            "$ref": "vault",
            "$id": "d4e5f6a7-b8c9-0123-defg-h45678901234"
          },
          "documents": [
            {
              "templateId": "tmpl_loan_agreement_v2",
              "signed": {
                "$ref": "vault",
                "$id": "e5f6a7b8-c9d0-1234-efgh-i56789012345"
              }
            }
          ]
        }
      }
    }
  ]
}